Cybersecurity protects your systems. Cybersecurity risk management protects your business.®

The Information Highway

The Information Highway

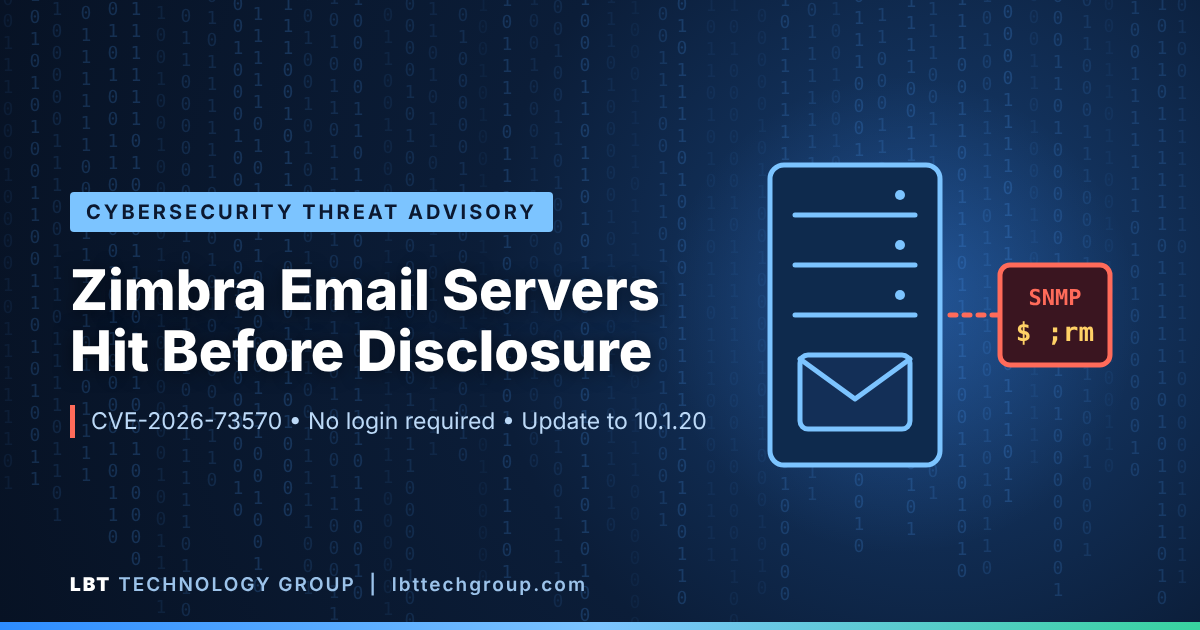
Zimbra Email Servers Hacked Before the Flaw Was Even Announced: What You Need to Know

img-zimbra
A fix for a critical Zimbra email server flaw was available for more than three weeks before the public was told about it, and attackers used that time. Microsoft Threat Intelligence reports that threat actors exploited CVE-2026-73570 (CVSS 8.9), an unauthenticated operating system command injection vulnerability in the Zimbra Collaboration Suite, for weeks before it was disclosed. The Shadowserver Foundation counted 274 compromised Zimbra servers in a single recent week.
Continue reading
  65 Hits

Critical Cisco SD-WAN Flaw Under Active Attack: What Business Owners Need to Do Now

img-cisco-sdwan
Cisco has confirmed that attackers are actively exploiting a critical vulnerability in the software many businesses use to connect their offices together. The flaw, tracked as CVE-2026-76504 and rated 9.8 out of 10 on the CVSS severity scale, affects Cisco Catalyst SD-WAN Manager. It lets a remote attacker slip past a login check and gain administrator-level access to a protected management API. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has already added it to its Known Exploited Vulnerabilities (KEV) catalog and gave federal agencies until October 3, 2026 to fix it.
Continue reading
  102 Hits

An AI Agent Hacked a Security Nonprofit Through Its Helpdesk: Lessons from the DIVD Breach

img-zammad
A cybersecurity nonprofit whose entire mission is warning others about vulnerabilities has itself been breached, and it believes an AI agent did the hacking. On September 24, 2026, the Dutch Institute for Vulnerability Disclosure (DIVD) announced that attackers had broken into its systems. Over the following week, DIVD revealed that the attacker exploited two previously unknown vulnerabilities in Zammad, a popular open-source helpdesk and ticketing system, and stole volunteer data. Zammad has not yet released official patches.
Continue reading
  100 Hits

Critical Citrix NetScaler Zero-Days Are Under Active Attack: What Your Business Needs to Do This Week

server-room-closeup-critical-error

A pair of critical, unauthenticated zero-day vulnerabilities in Citrix NetScaler are being actively exploited right now and with roughly 23,000 internet-exposed devices worldwide, this is a "patch today, not next sprint" moment that shows exactly why continuous vulnerability management can't be a once-a-quarter checkbox for any growing business.

Continue reading
  155 Hits

Cybersecurity Threat Advisory: WordPress "Click2Shell" Flaw Turns One Admin Click into Full Site Takeover

Threat-Advisory-Banner3

Threat update

A newly disclosed vulnerability in WordPress Core, nicknamed Click2Shell, allows an attacker to take control of a WordPress website if a logged-in administrator simply opens a specially crafted link. No further clicks, prompts, or approvals are needed. WordPress fixed the issue in version 7.1.1 and backported the fix to every supported branch back to 4.7. Because proof-of-concept code is now public, any organization running WordPress should confirm its sites are updated today.

Continue reading
  154 Hits

Top Breaches Cost ($) of 2024

HEALTHCARE
FINANCIAL
INDUSTRIAL
TECHNOLOGY
ENERGY
Source: IBM Cost of a Data Breach Report 2024