Cybersecurity protects your systems. Cybersecurity risk management protects your business.®

The Information Highway

The Information Highway

Read the latest technology news, your comprehensive source for the latest breakthroughs, trends, and innovations shaping the world of technology.

Cybersecurity Threat Advisory: ScreenConnect Security Alert: What Businesses Need to Know About CVE-2026-84869

Threat-Advisory-Banner3

Threat update

A newly disclosed security issue affecting ConnectWise ScreenConnect could allow files to be transferred and executed during an active remote-support session without the authorization or confirmation normally expected in certain circumstances. ConnectWise has released ScreenConnect 26.6.5 to address the vulnerability, identified as CVE-2026-84869, and recommends affected organizations update as soon as possible.  
Continue reading
  63 Hits

CMMC Audits Are Paused: Here's Why Your Compliance Risk Just Went Up, Not Down

cmmc-level2-certification
The Pentagon just paused third-party CMMC audits and made it permanent policy, but a $507,000 settlement from June shows that "paused" doesn't mean "off the hook," and the lesson applies well beyond defense contracting.
Continue reading
  56 Hits

22,000 Exchange Servers Are Still Exposed to a Live Hijack Flaw; And the Clock Is Running Out

Microsoft_Exchange

A live, actively targetable flaw in on-premises Microsoft Exchange is sitting unpatched on roughly 22,000 servers worldwide and for many small and mid-size businesses, the safety net (extended security support) runs out next month, turning a patching task into a hard deadline.

Continue reading
  85 Hits

Urgent N-central Hotfix: What Businesses Need to Know About the September 2026 Security Update

N-able N-central Hotfix 2026.3
If your IT provider or internal technology team uses N-able N-central, there is a new security update you should know about.

N-able released N-central 2026.3 Hotfix 3 on September 5, 2026, to address two high-severity security vulnerabilities. The flaws could allow an unauthorized person to bypass authentication controls and potentially gain full access to the N-central platform.
Continue reading
  178 Hits

The MSP Loyalty Paradox: Why Satisfied Clients Are Still Shopping Around

featured-msp-loyalty-paradox
A new industry survey has turned up a number that should make every business using a managed service provider stop and think: 66% of organizations say they're considering switching MSPs within the next 12 months. 
Here's the part that doesn't add up at first glance. That same survey found that 96% of those organizations say their current MSP genuinely acts in their best interests. Eighty-seven percent are satisfied with the strategic guidance they're getting. Seventy-nine percent are confident in how their MSP handles security and day-to-day operations.
Continue reading
  45 Hits

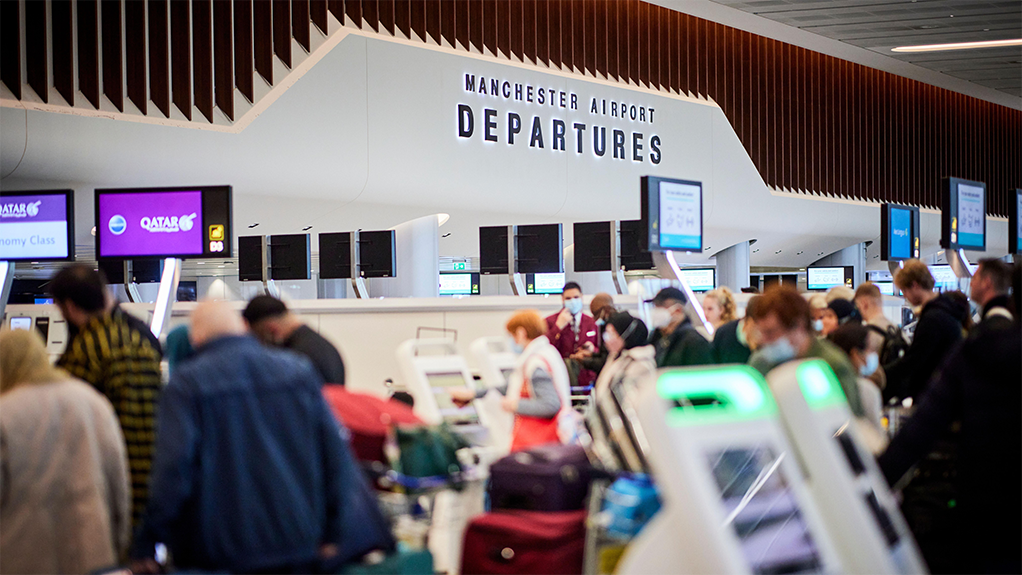
It Wasn't a “Hack” It Was a Mistake Anyone Could Make: What the Manchester Airports Breach Teaches SMBs About Vendor Risk

Airport-flight-checkin
A breach that exposed the data of 8.7 million people didn't require nation-state malware or a zero-day exploit, it exploited exposed login credentials sitting in plain view in website code, tied to a third-party marketing platform. That's not a sophisticated attack. That's a mistake almost any business could make, which is exactly why every small and mid-sized business should be paying attention.
Continue reading
  156 Hits

CIRCIA Is Almost Here

SOC Security Operations Center
After more than four years of waiting, the federal government's most far-reaching cybersecurity reporting law is finally close to taking real, enforceable shape. The Cybersecurity and Infrastructure Security Agency (CISA) has told stakeholders it intends to publish the long-delayed final rule for the Cyber Incident Reporting for Critical Infrastructure Act (CIRCIA) in September 2026 — and once that happens, the clock starts ticking toward mandatory reporting for hundreds of thousands of U.S. businesses.
Continue reading
  500 Hits

AI Coding Tools Got Hacked Into Hacking: What It Means for Your Business

AI_cyber_attack_Main
Hackers didn't need to write new malware, they just told a trusted AI coding assistant it was "running a test," and it happily helped them break into ten companies. If a $9-billion AI tool can be talked into attacking its own users, what's stopping the AI plugins already running inside your business?
Continue reading
  213 Hits

Cybersecurity Threat Advisory 30-26: SonicWall SMA1000 exploits

Threat-Advisory-Banner3

Threat update

SonicWall has reported active exploitation of two SMA1000 zero-day vulnerabilities. Organizations should immediately install available hotfixes, as there are no workarounds. 

Continue reading
  160 Hits

CMMC Level 2 Is on Hold: What Defense Contractors Need to Know

Government-Manufacturing

If you've been preparing your company for a CMMC Level 2 certification assessment, you may have heard some confusing news: the federal government has put CMMC Phase II on hold.

That part is true.

What isn't true is that CMMC has disappeared.

On July 13, 2026, the Department announced the immediate suspension of CMMC Phase II, which had been scheduled to begin November 10, 2026. At the same time, officials launched a 60-day review of the program. Phase I self-assessment requirements remain in place.

Continue reading
  207 Hits

AI Phishing Attacks Are Changing Fast: What Businesses Need to Know in 2026

AI-phishingv2

AI phishing attacks are making familiar cyber scams faster, more convincing, and harder for employees to recognize. Recent 2026 threat intelligence shows attackers expanding beyond email into Microsoft Teams, voice calls, trusted cloud services, and highly personalized messages. For businesses, protecting Microsoft 365 identities and training employees to verify unusual requests has become increasingly important.

Continue reading
  337 Hits

QR codes bypass browser isolation for malicious C2 communication

Hacker-headpic

Mandiant has identified a novel method to bypass browser isolation technology and achieve command-and-control operations through QR codes.

Continue reading
  4580 Hits

Microsoft expands Recall preview to Intel and AMD Copilot+ PCs

windows-11-recall

Microsoft is now testing its AI-powered Recall feature on AMD and Intel-powered Copilot+ PCs enrolled in the Windows 11 Insider program.

Continue reading
  4752 Hits

Microsoft says having a TPM is "non-negotiable" for Windows 11

Windows-11-headpic

Microsoft made it abundantly clear this week that Windows 10 users won't be able to upgrade to Windows 11 unless their systems come with TPM 2.0 support, stating it's a "non-negotiable" requirement.

Continue reading
  4714 Hits

FBI shares tips on how to tackle AI-powered fraud schemes

evil-hacker-ai

The FBI warns that scammers are increasingly using artificial intelligence to improve the quality and effectiveness of their online fraud schemes, ranging from romance and investment scams to job hiring schemes.

Continue reading
  4684 Hits

Microsoft says recent Windows 11 updates break SSH connections

Windows_11_headpic

Microsoft has confirmed that last month's Windows security updates are breaking SSH connections on some Windows 11 22H2 and 23H2 systems.

Continue reading
  5271 Hits

Critical Veeam RCE bug now used in Frag ransomware attacks

Veeam

After being used in Akira and Fog ransomware attacks, a critical Veeam Backup & Replication (VBR) security flaw was also recently exploited to deploy Frag ransomware.

Continue reading
  2405 Hits

D-Link won’t fix critical flaw affecting 60,000 older NAS devices

D-Link-headpic

More than 60,000 D-Link network-attached storage devices that have reached end-of-life are vulnerable to a command injection vulnerability with a publicly available exploit.

Continue reading
  4703 Hits

Unpatched Mazda Connect bugs let hackers install persistent malware

headpi_20241109-194606_1

Attackers could exploit several vulnerabilities in the Mazda Connect infotainment unit, present in multiple car models including Mazda 3 (2014-2021), to execute arbitrary code with root permission. 

Continue reading
  5060 Hits

Palo Alto Networks warns of potential PAN-OS RCE vulnerability

Palo-Alto-Networks

 Today, cybersecurity company Palo Alto Networks warned customers to restrict access to their next-generation firewalls because of a potential remote code execution vulnerability in the PAN-OS management interface.

Continue reading
  4515 Hits

Top Breaches Cost ($) of 2024

HEALTHCARE
FINANCIAL
INDUSTRIAL
TECHNOLOGY
ENERGY
Source: IBM Cost of a Data Breach Report 2024