Ivanti has fixed a maximum severity vulnerability in its Endpoint Management software (EPM) that can let unauthenticated attackers gain remote code execution on the core server.
We have some good news to share: as of Wednesday, September 30, 2026, LBT Technology Group, LLC is officially SPECTRA Certified.
If you've never heard of SPECTRA, you're not alone. Most business owners don't spend their days thinking about IT certifications, and they shouldn't have to. That's our job. But this one is worth a few minutes of your time, because it affects how well your business is protected, and it may even lower what you pay for cyber insurance.
In this post, we'll explain what SPECTRA Certification is, what we had to prove to earn it, and what it means for you, whether you're already a client or you're looking for an IT partner.
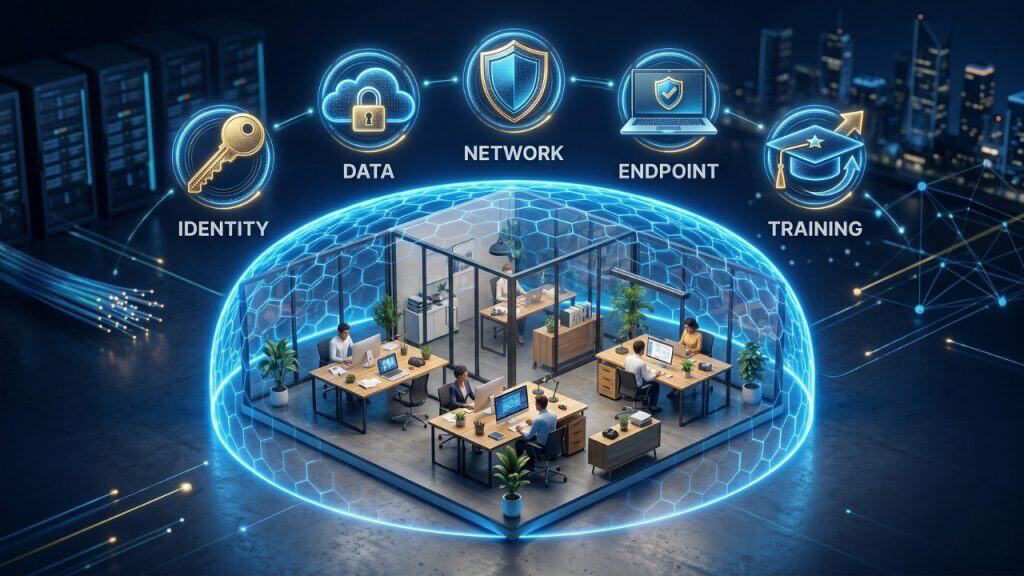
A live, actively targetable flaw in on-premises Microsoft Exchange is sitting unpatched on roughly 22,000 servers worldwide and for many small and mid-size businesses, the safety net (extended security support) runs out next month, turning a patching task into a hard deadline.
Ivanti has fixed a maximum severity vulnerability in its Endpoint Management software (EPM) that can let unauthenticated attackers gain remote code execution on the core server.
There were recently six vulnerabilities discovered in Veeam Backup and Replication. One of them is an unauthenticated remote code execution (RCE), while the other five include authenticated RCE, arbitrary file deletion, low-privileged multi-factor authentication (MFA) setting modification and MFA bypass, credential sniffing, and privilege escalation. Review the details in this Cybersecurity Threat Advisory to limit customers' impact.
Progress Software has issued an emergency fix for a maximum (10/10) severity vulnerability impacting its LoadMaster and LoadMaster Multi-Tenant (MT) Hypervisor products that allows attackers to remotely execute commands on the device.
A novel side-channel attack dubbed "RAMBO" (Radiation of Air-gapped Memory Bus for Offense) generates electromagnetic radiation from a device's RAM to send data from air-gapped computers.
American car rental giant Avis notified customers that unknown attackers breached one of its business applications last month and stole some of their personal information.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.