Threat actors claim to be selling 3TB of data from Advance Auto Parts, a leading automotive aftermarket parts provider, stolen after breaching the company's Snowflake account.
We have some good news to share: as of Wednesday, September 30, 2026, LBT Technology Group, LLC is officially SPECTRA Certified.
If you've never heard of SPECTRA, you're not alone. Most business owners don't spend their days thinking about IT certifications, and they shouldn't have to. That's our job. But this one is worth a few minutes of your time, because it affects how well your business is protected, and it may even lower what you pay for cyber insurance.
In this post, we'll explain what SPECTRA Certification is, what we had to prove to earn it, and what it means for you, whether you're already a client or you're looking for an IT partner.
A live, actively targetable flaw in on-premises Microsoft Exchange is sitting unpatched on roughly 22,000 servers worldwide and for many small and mid-size businesses, the safety net (extended security support) runs out next month, turning a patching task into a hard deadline.
Threat actors claim to be selling 3TB of data from Advance Auto Parts, a leading automotive aftermarket parts provider, stolen after breaching the company's Snowflake account.
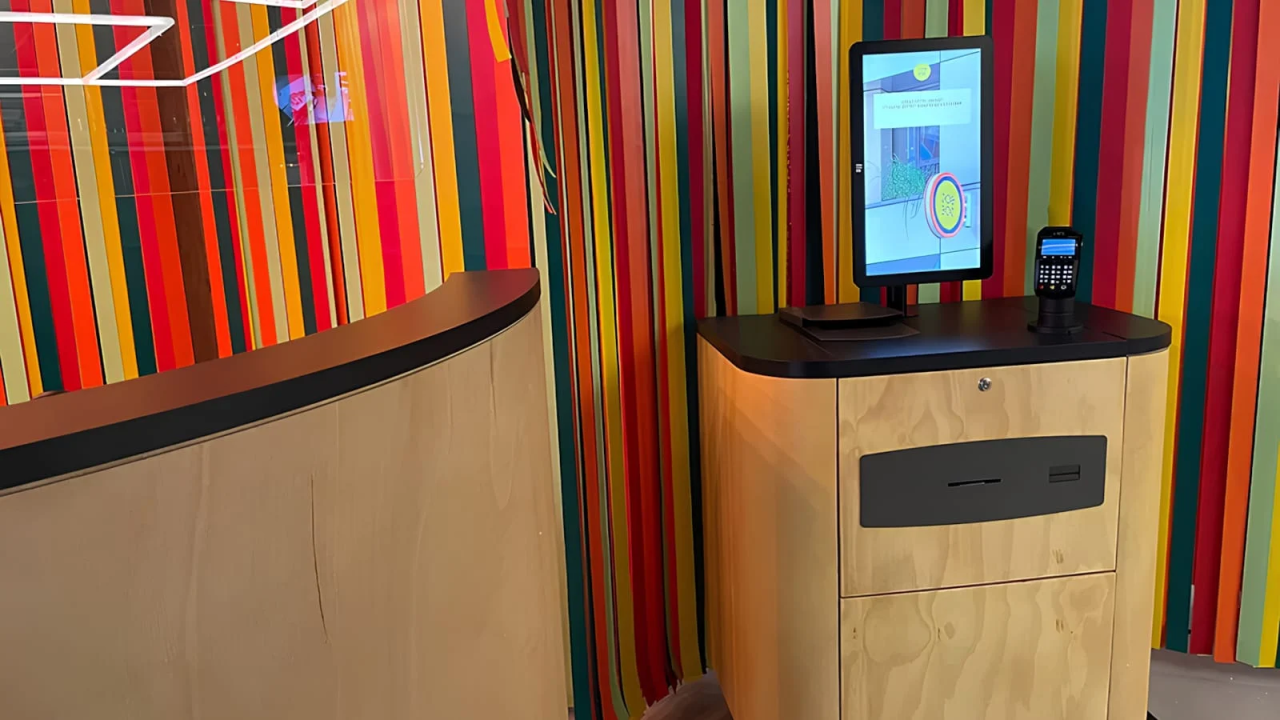
Ariane Systems self check-in systems installed at thousands of hotels worldwide are vulnerable to a kiosk mode bypass flaw that could allow access to guests' personal information and the keys for other rooms.
ShrinkLocker is a recent ransomware strain that leverages a legitimate Windows encryption feature, BitLocker, to lock victims out of their devices. It shrinks the partition, increasing the impact of the attack.
There has been active exploitation of a critical operating system (OS) command injection vulnerability, known as CVE-2017-3506, found in the Oracle WebLogic Server. The impact can be severe, ranging from financial loss to reputational damage.
A new critical command injection vulnerability, CVE-2024-23108, was found in Fortinet's FortiSIEM solution. This vulnerability poses significant risks to organizations using the solution.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.