The U.S. Cybersecurity & Infrastructure Security Agency (CISA) has added three security vulnerabilities to its 'Known Exploited Vulnerabilities' catalog, one impacting Google Chrome and two affecting some D-Link routers.
We have some good news to share: as of Wednesday, September 30, 2026, LBT Technology Group, LLC is officially SPECTRA Certified.
If you've never heard of SPECTRA, you're not alone. Most business owners don't spend their days thinking about IT certifications, and they shouldn't have to. That's our job. But this one is worth a few minutes of your time, because it affects how well your business is protected, and it may even lower what you pay for cyber insurance.
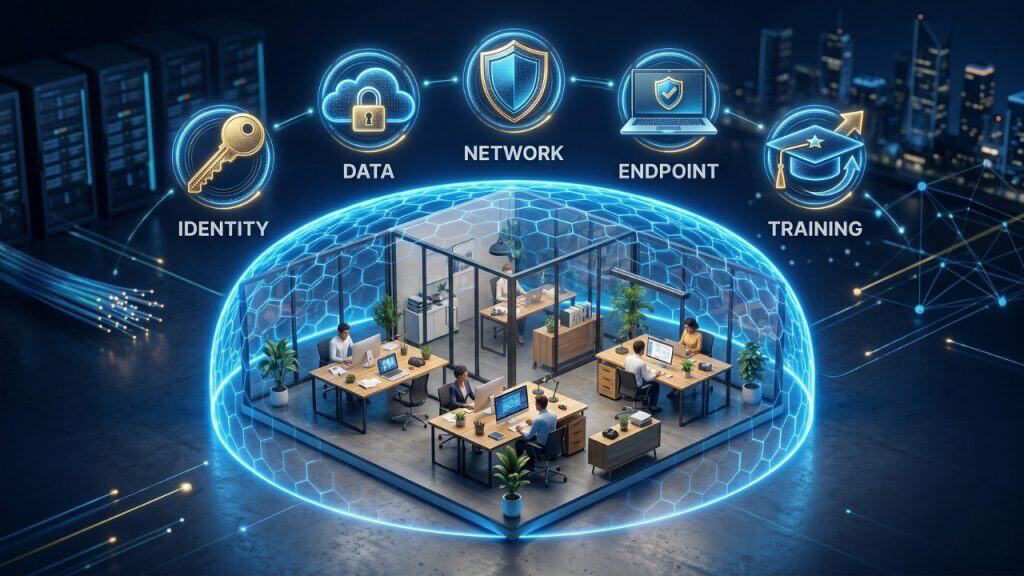
In this post, we'll explain what SPECTRA Certification is, what we had to prove to earn it, and what it means for you, whether you're already a client or you're looking for an IT partner.
A live, actively targetable flaw in on-premises Microsoft Exchange is sitting unpatched on roughly 22,000 servers worldwide and for many small and mid-size businesses, the safety net (extended security support) runs out next month, turning a patching task into a hard deadline.
The U.S. Cybersecurity & Infrastructure Security Agency (CISA) has added three security vulnerabilities to its 'Known Exploited Vulnerabilities' catalog, one impacting Google Chrome and two affecting some D-Link routers.
A ransomware operation targets Windows system administrators by taking out Google ads to promote fake download sites for Putty and WinSCP.
Starting in July, Microsoft will begin gradually enforcing multi-factor authentication (MFA) for all users signing into Azure to administer resources.
The Securities and Exchange Commission (SEC) has adopted amendments to Regulation S-P that require certain financial institutions to disclose data breach incidents to impacted individuals within 30 days of discovery.
The WebTPA Employer Services (WebTPA) data breach disclosed earlier this month is impacting close to 2.5 million individuals, the U.S. Department of Health and Human Services notes.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.