A threat actor is using fake LinkedIn posts and direct messages about a Facebook Ads specialist position at hardware maker Corsair to lure people into downloading info-stealing malware like DarkGate and RedLine.
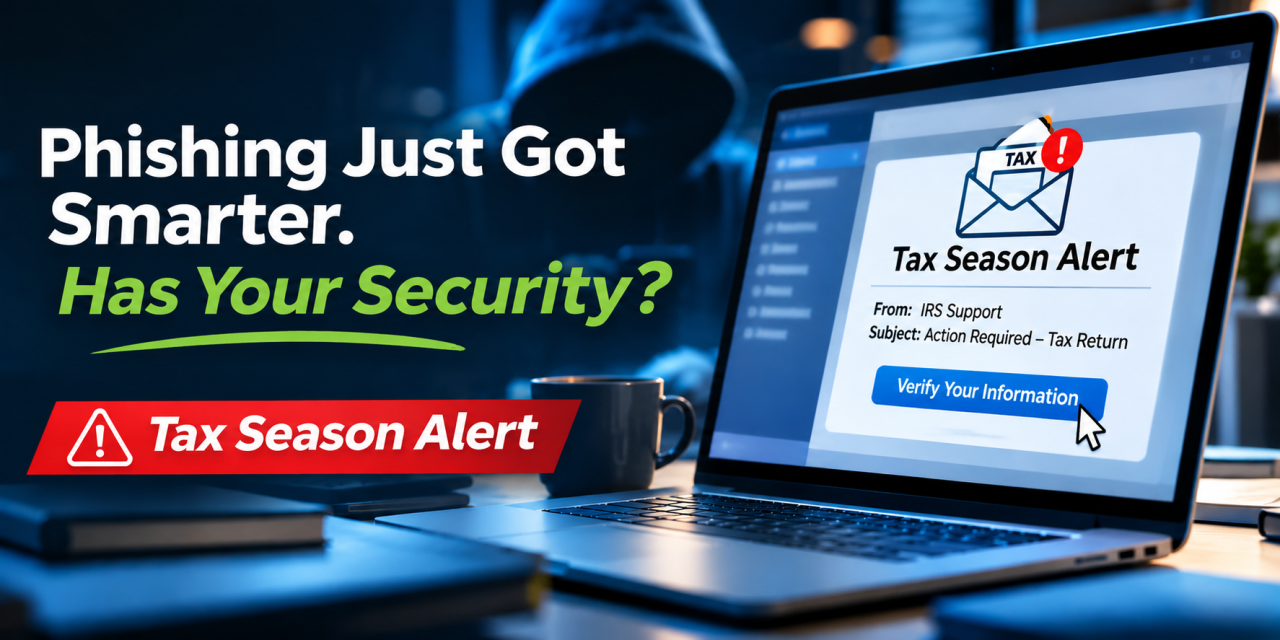
This week, NIST published its first cybersecurity guide written specifically for businesses too small to have an IT department and days later, CISA confirmed active exploitation of a VPN flaw sitting on firewalls many of those same businesses rely on, proving the guidance couldn't have arrived at a better time.
When a single ransomware attack can cancel surgeries, divert ambulances, and cancel classes within hours, "we're too small to be a target" stops being a credible security strategy for any organization including yours.
We have some good news to share: as of Wednesday, September 30, 2026, LBT Technology Group, LLC is officially SPECTRA Certified.
If you've never heard of SPECTRA, you're not alone. Most business owners don't spend their days thinking about IT certifications, and they shouldn't have to. That's our job. But this one is worth a few minutes of your time, because it affects how well your business is protected, and it may even lower what you pay for cyber insurance.
In this post, we'll explain what SPECTRA Certification is, what we had to prove to earn it, and what it means for you, whether you're already a client or you're looking for an IT partner.
A threat actor is using fake LinkedIn posts and direct messages about a Facebook Ads specialist position at hardware maker Corsair to lure people into downloading info-stealing malware like DarkGate and RedLine.
More than 40,000 Cisco devices running the IOS XE operating system have been compromised after hackers exploited a recently disclosed maximum severity vulnerability tracked as CVE-2023-20198.
The BlackCat/ALPHV ransomware operation has begun to use a new tool named 'Munchkin' that utilizes virtual machines to deploy encryptors on network devices stealthily.

A Google Ads campaign was found pushing a fake KeePass download site that used Punycode to appear as the official domain of the KeePass password manager to distribute malware.
India's Central Bureau of Investigation (CBI) raided 76 locations in a nationwide crackdown on cybercrime operations behind tech support scams and cryptocurrency fraud.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.