An updated version of the MATA backdoor framework was spotted in attacks between August 2022 and May 2023, targeting oil and gas firms and the defense industry in Eastern Europe.
An updated version of the MATA backdoor framework was spotted in attacks between August 2022 and May 2023, targeting oil and gas firms and the defense industry in Eastern Europe.
Hackers are scanning for internet-exposed Jupyter Notebooks to breach servers and deploy a cocktail of malware consisting of a Linux rootkit, crypto miners, and password-stealing scripts.

Between July and September, DarkGate malware attacks have used compromised Skype accounts to infect targets through messages containing VBA loader script attachments.
Apple has published security updates for older iPhones and iPads to backport patches released one week ago, addressing two zero-day vulnerabilities exploited in attacks.
Shadow PC, a provider of high-end cloud computing services, is warning customers of a data breach that exposed customers' private information, as a threat actor claims to be selling the stolen data for over 500,000 customers.
A new malware has been posing as a legitimate caching plugin to target WordPress sites, allowing threat actors to create an administrator account and control the site's activity.
Microsoft Defender for Endpoint now uses automatic attack disruption to isolate compromised user accounts and block lateral movement in hands-on-keyboard attacks with the help of a new 'contain user' capability in public preview.
Microsoft says a Chinese-backed threat group tracked as 'Storm-0062' (aka DarkShadow or Oro0lxy) has been exploiting a critical privilege escalation zero-day in the Atlassian Confluence Data Center and Server since September 14, 2023.
Hackers are once again abusing LinkedIn Smart Links in phishing attacks to bypass protection measures and evade detection in attempts to steal Microsoft account credentials.
Microsoft warned customers this week of incorrect BitLocker drive encryption errors being shown in some managed Windows environments.

A Mirai-based DDoS (distributed denial of service) malware botnet tracked as IZ1H9 has added thirteen new payloads to target Linux-based routers and routers from D-Link, Zyxel, TP-Link, TOTOLINK, and others.
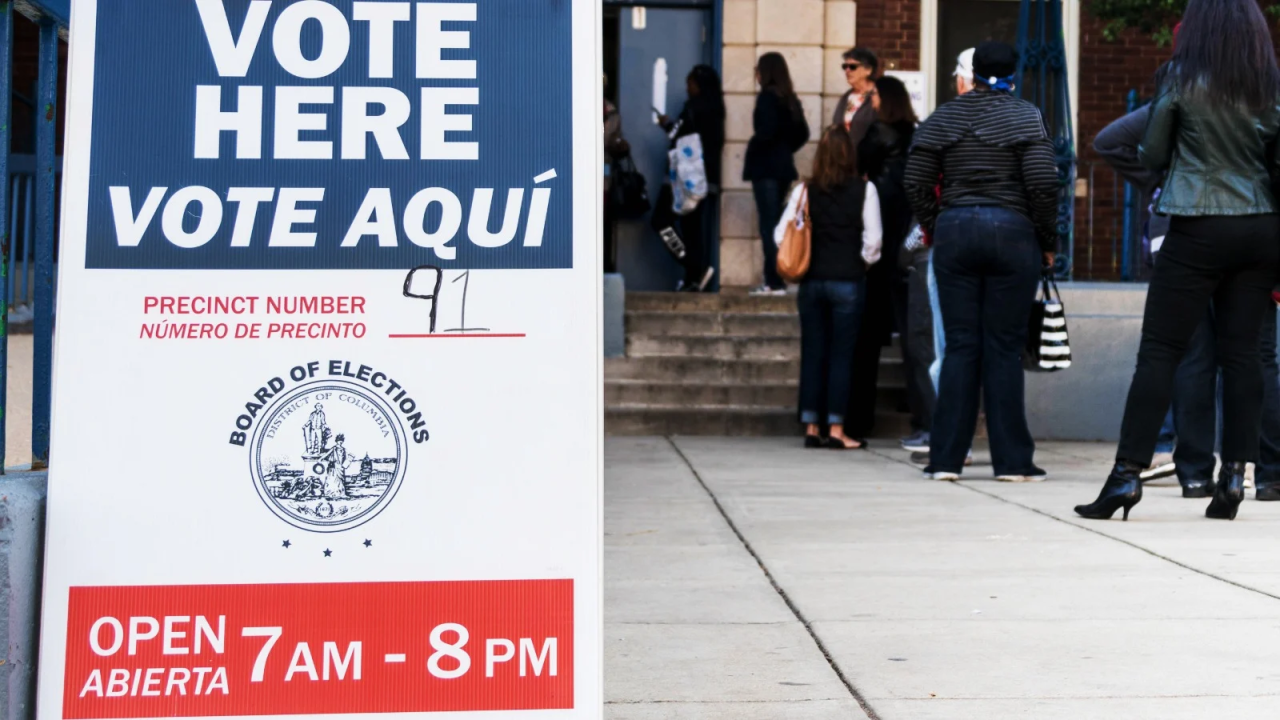
The District of Columbia Board of Elections (DCBOE) is currently probing a data leak involving an unknown number of voter records following breach claims from a threat actor known as RansomedVC.
23andMe has confirmed that it is aware of user data from its platform circulating on hacker forums and attributes the leak to a credential-stuffing attack.
Hackers engaging in cyber espionage have targeted Chinese-speaking semiconductor companies with TSMC-themed lures that infect them with Cobalt Strike beacons.
The National Security Agency (NSA) and the Cybersecurity and Infrastructure Security Agency (CISA) revealed today the top ten most common cybersecurity misconfigurations discovered by their red and blue teams in the networks of large organizations.
Lyca Mobile has released a statement about an unexpected disruption on its network caused by a cyberattack that may have also compromised customer data.
Apple released new emergency security updates on Wednesday to patch two new zero-day vulnerabilities known to be exploited in attacks.
Hackers have been observed trying to breach cloud environments through Microsoft SQL Servers vulnerable to SQL injection.
Sony Interactive Entertainment (Sony) has notified current and former employees and their family members about a cybersecurity breach that exposed personal information.
Microsoft's new Azure Active Directory Cross-Tenant Synchronization (CTS) feature, introduced in June 2023, has created a new potential attack surface that might allow threat actors to more easily spread laterally to other Azure tenants.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.