Cybersecurity protects your systems. Cybersecurity risk management protects your business.®

The Information Highway

The Information Highway

The Payment That Never Arrived: Tax Season, AI Phishing, and the MFA Decision That Cost

Tax-Season-Phishing-Alert
Every year, the weeks between January and April turn inboxes into a minefield. W-2s go out. Accountants request documents. Payroll providers send notices. Vendors chase invoices before the books close. It's the busiest, most paperwork-heavy stretch of the year, and cybercriminals plan for it just like your finance team does.
Continue reading
  220 Hits

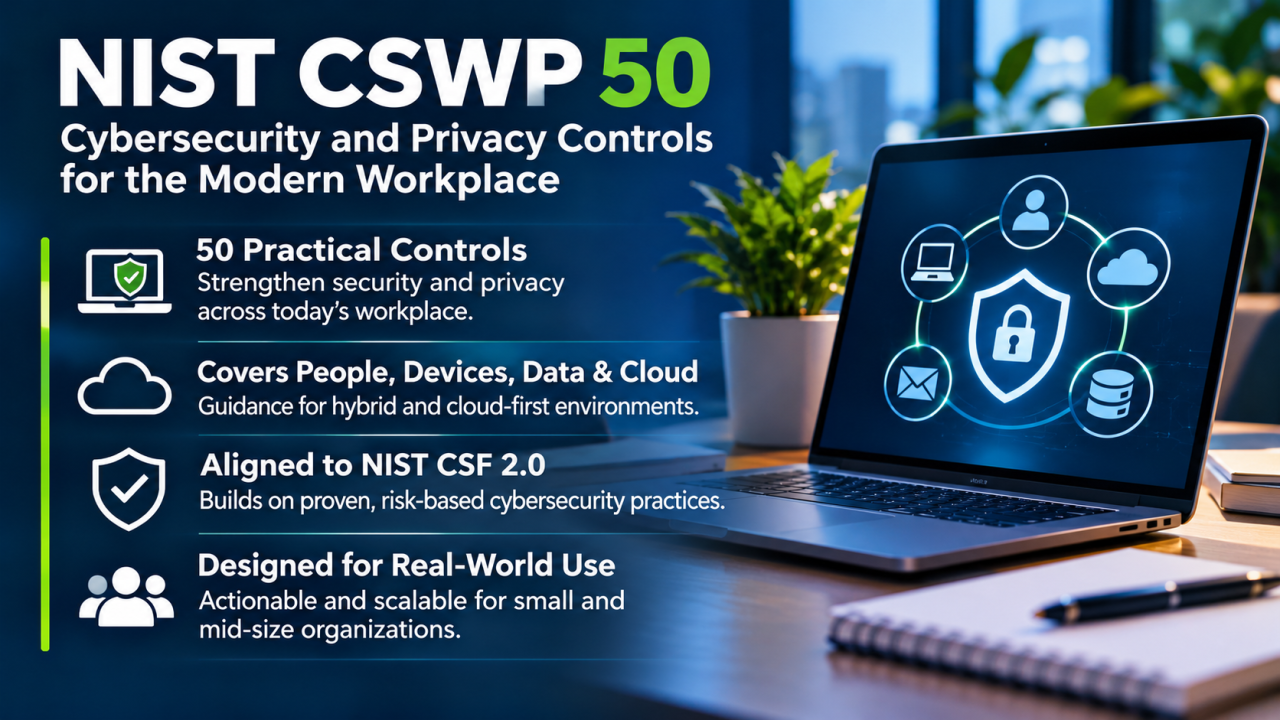
NIST’s New Small Business Guide Lands the Same Week a Live VPN Threat Proves Why It Matters

NIST-CSWP-50_-Modern-Workplace-Securit_20261111-000020_1

This week, NIST published its first cybersecurity guide written specifically for businesses too small to have an IT department and days later, CISA confirmed active exploitation of a VPN flaw sitting on firewalls many of those same businesses rely on, proving the guidance couldn't have arrived at a better time.

Continue reading
  324 Hits

When a Hospital Goes Dark: What the UNM Health Ransomware Attack Teaches Every SMB About Cyber Risk and Compliance

Red-Alert-in-the-Server-Roo_20261103-032438_1

When a single ransomware attack can cancel surgeries, divert ambulances, and cancel classes within hours, "we're too small to be a target" stops being a credible security strategy for any organization including yours.

Continue reading
  815 Hits

Your Backups Are the Target Now: What This Week's SafePay Ransomware Advisory Means for Your Business

data-backup
Federal agencies just confirmed that one of 2026's most active ransomware gangs doesn't just encrypt your data it hunts down and deletes your backups first, which means "we have backups" is no longer a safety net unless those backups are built to survive the attack itself.
Continue reading
  600 Hits

Your MFA Didn't Fail You, Your Session Did: Inside the 79-Company Microsoft 365 Breach

hero_image

Employees did everything security training told them to do typed the password, approved the MFA prompt, and attackers walked into their inbox anyway, because this attack never needed to beat MFA at all; it just stole the session that came after it.

Continue reading
  596 Hits

When “Fully Patched” Isn’t Enough

CybersecurityUpdateDashboard
In a single week, Microsoft shipped a record-shattering 1,400+ patches, attackers breached a VPN appliance that was already fully up to date, and CISA added nine actively exploited flaws to its must-patch list a stark reminder that for small and mid-sized businesses, "we installed the updates" is no longer the same thing as "we're secure."
Continue reading
  718 Hits

AI Supply Chain Security: Is Your Business Trusting Tools Noone Has Checked?

ai-supply-chain-security-business

AI supply chain security means protecting your business from risks introduced by artificial intelligence tools, their connected applications, and outside services. An AI assistant may seem like just another productivity tool, but when it can access company email, files, customer records, or business systems, it becomes another connection that needs to be managed and protected.

Continue reading
  727 Hits

LBT Technology Group Is Now SPECTRA Certified: What It Means for You

Spectra-Certified-Asset-29-Colour-300ppi

We have some good news to share: as of Wednesday, September 30, 2026, LBT Technology Group, LLC is officially SPECTRA Certified.

If you've never heard of SPECTRA, you're not alone. Most business owners don't spend their days thinking about IT certifications, and they shouldn't have to. That's our job. But this one is worth a few minutes of your time, because it affects how well your business is protected, and it may even lower what you pay for cyber insurance.

In this post, we'll explain what SPECTRA Certification is, what we had to prove to earn it, and what it means for you, whether you're already a client or you're looking for an IT partner.

Continue reading
  1192 Hits

Your Team's "Vibe Coded" App Might Already Be Leaking Customer Data

Holographic-Shield-Over-Server-Rack_20261008-101250_1

A single security scan this week found over 16,000 publicly exposed databases built with AI coding tools — a wake-up call that the rush to build fast with AI is quietly creating a breach crisis for businesses of every size, not just tech giants.

Continue reading
  1174 Hits

Remote Access Is This Week's Battleground: Here's What Your Business Needs to Know

remoge_access_featured_image
Two fresh warnings, a SANS-flagged wave of attacks abusing legitimate remote-support software and a newly exploited Citrix NetScaler zero-day with a federal patch deadline this week, both target the exact remote-access tools SMBs and their IT providers rely on every day.
Continue reading
  968 Hits

Cybersecurity Threat Advisory: ScreenConnect Security Alert: What Businesses Need to Know About CVE-2026-84869

Threat-Advisory-Banner3

Threat update

A newly disclosed security issue affecting ConnectWise ScreenConnect could allow files to be transferred and executed during an active remote-support session without the authorization or confirmation normally expected in certain circumstances. ConnectWise has released ScreenConnect 26.6.5 to address the vulnerability, identified as CVE-2026-84869, and recommends affected organizations update as soon as possible.  

Continue reading
  1141 Hits

Cybersecurity Threat Advisory: TrustSink Turns Microsoft Entra ID's MFA Against You to Steal Passwords

Threat-Advisory-Banner3

Threat update

Researchers have demonstrated a new attack technique called TrustSink that abuses the multi-factor authentication (MFA) features in Microsoft Entra ID, the identity service behind Microsoft 365. An attacker who gains control of a high-level admin account can quietly add a fake MFA provider to the tenant. From then on, every time a user signs in, that fake provider captures their password in plain text while the login completes normally. Organizations that use Microsoft 365 should review their Entra ID authentication settings and lock down admin accounts now.

Continue reading
  979 Hits

"The AI Did It" Is Not a Defense: What the OpenAI Lawsuit Means for Businesses Using AI Agents

img-ai-accountability
AI agents are quickly moving from experiment to everyday business tool, and a new lawsuit is a timely reminder that when an AI agent causes harm, someone is still responsible. On September 29, 2026, the nonprofit Legal Advocates for Safe Science and Technology (LASST) sued OpenAI in California, seeking to hold the company accountable for the actions of its AI agents, including their role in the July 2026 breach of Hugging Face. At the center of the case is a California law that took effect this year and says, in effect, that "the AI did it" is not a legal defense.
Continue reading
  1107 Hits

Critical Citrix NetScaler Zero-Days Are Under Active Attack: What Your Business Needs to Do This Week

server-room-closeup-critical-error

A pair of critical, unauthenticated zero-day vulnerabilities in Citrix NetScaler are being actively exploited right now and with roughly 23,000 internet-exposed devices worldwide, this is a "patch today, not next sprint" moment that shows exactly why continuous vulnerability management can't be a once-a-quarter checkbox for any growing business.

Continue reading
  915 Hits

Your Backups Might Not Save You: What a New Ransomware Recovery Study Means for Small and Mid-Sized Businesses

broken-chain-link-backup-recovery
A new field study of 800+ real-world ransomware recoveries found that only four organizations hit their 24-48 hour recovery target — and the reason usually wasn't missing backups, it was an untested, incomplete recovery plan.
Continue reading
  824 Hits

Cybersecurity Threat Advisory: ZcopyReaper Linux Kernel Flaw Gives Local Users Root Access, and Exploit Code Is Public

Threat-Advisory-Banner3

Threat update

A newly detailed Linux kernel vulnerability, tracked as CVE-2026-43502 and nicknamed ZcopyReaper, allows an unprivileged local user to escalate to full root control by abusing a memory-handling error in the kernel's Reliable Datagram Sockets (RDS) component. The flaw has existed since Linux kernel 4.17, working exploit code has been published, and patched kernels are available from major distributions. Organizations running Linux servers, cloud workloads, or Linux-based appliances should confirm patch status now. 

Continue reading
  850 Hits

Cybersecurity Threat Advisory: KATARU Malware Is Turning Exposed IoT Devices into Long-Term DDoS Bots

Threat-Advisory-Banner3

Threat update

A newly documented malware family named KATARU is hijacking internet-facing Linux devices, including routers and other IoT equipment, by guessing weak or default Telnet passwords. Once inside, it takes root-level control, embeds itself so it survives reboots, and enlists the device in a Mirai-style botnet used for large-scale DDoS attacks. Any organization with connected devices that are exposed to the internet, unpatched, or protected by default credentials should review its exposure now.

Continue reading
  868 Hits

Business Continuity and Disaster Recovery: Could Your Business Keep Running Tomorrow?

business-continuity-disaster-recovery
Data BackupBackups aren't the whole recovery plan. Learn how business continuity and disaster recovery help protect your operations when technology fails.
Continue reading
  881 Hits

Urgent N-central Hotfix: What Businesses Need to Know About the September 2026 Security Update

N-able N-central Hotfix 2026.3
If your IT provider or internal technology team uses N-able N-central, there is a new security update you should know about.

N-able released N-central 2026.3 Hotfix 3 on September 5, 2026, to address two high-severity security vulnerabilities. The flaws could allow an unauthorized person to bypass authentication controls and potentially gain full access to the N-central platform.
Continue reading
  999 Hits

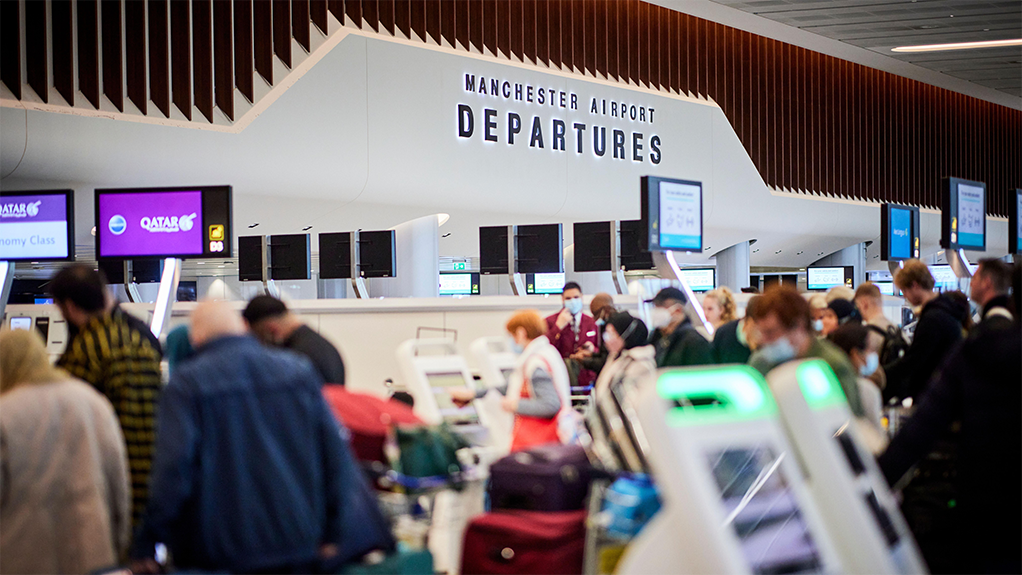
It Wasn't a “Hack” It Was a Mistake Anyone Could Make: What the Manchester Airports Breach Teaches SMBs About Vendor Risk

Airport-flight-checkin
A breach that exposed the data of 8.7 million people didn't require nation-state malware or a zero-day exploit, it exploited exposed login credentials sitting in plain view in website code, tied to a third-party marketing platform. That's not a sophisticated attack. That's a mistake almost any business could make, which is exactly why every small and mid-sized business should be paying attention.
Continue reading
  821 Hits

Top Breaches Cost ($) of 2024

HEALTHCARE
FINANCIAL
INDUSTRIAL
TECHNOLOGY
ENERGY
Source: IBM Cost of a Data Breach Report 2024