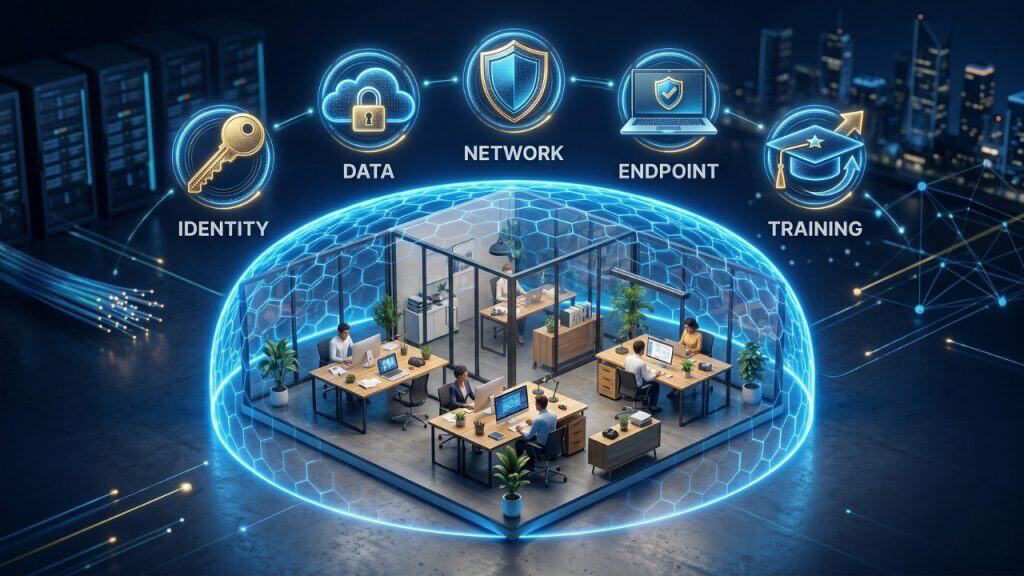
This week, NIST published its first cybersecurity guide written specifically for businesses too small to have an IT department and days later, CISA confirmed active exploitation of a VPN flaw sitting on firewalls many of those same businesses rely on, proving the guidance couldn't have arrived at a better time.
When a single ransomware attack can cancel surgeries, divert ambulances, and cancel classes within hours, "we're too small to be a target" stops being a credible security strategy for any organization including yours.
A live, actively targetable flaw in on-premises Microsoft Exchange is sitting unpatched on roughly 22,000 servers worldwide and for many small and mid-size businesses, the safety net (extended security support) runs out next month, turning a patching task into a hard deadline.
A cyberattack on CTS, a leading managed service provider (MSP) for law firms and other organizations in the UK legal sector, is behind a major outage impacting numerous law firms and home buyers in the country since Wednesday.