Cybersecurity protects your systems. Cybersecurity risk management protects your business.®

The Information Highway

The Information Highway

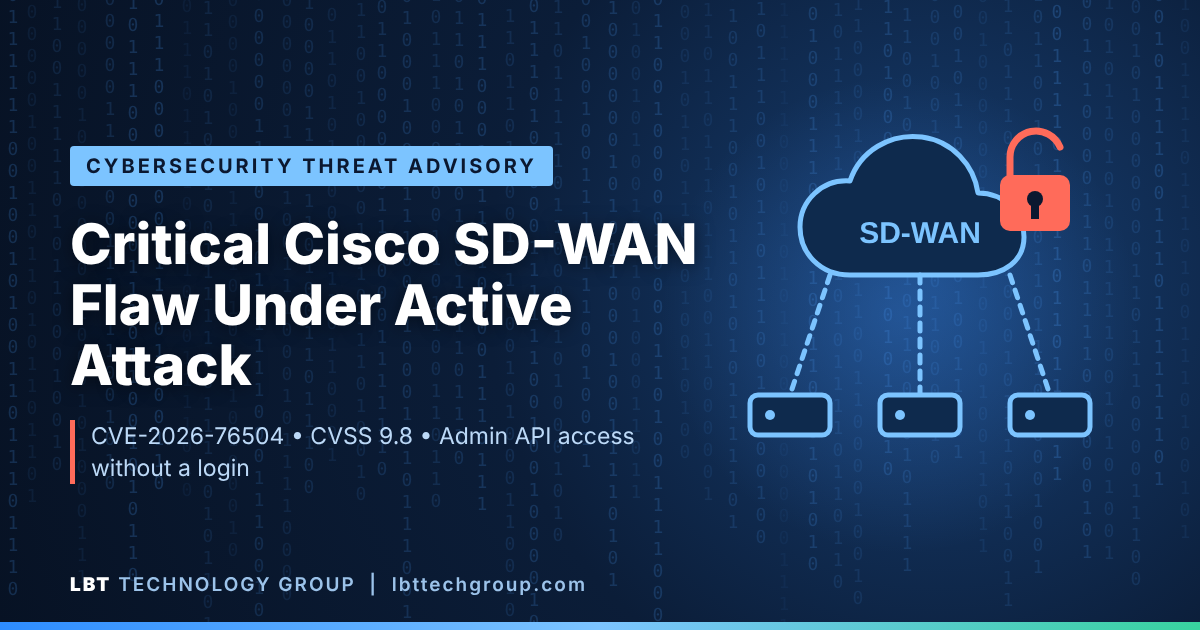
Critical Cisco SD-WAN Flaw Under Active Attack: What Business Owners Need to Do Now

img-cisco-sdwan
Cisco has confirmed that attackers are actively exploiting a critical vulnerability in the software many businesses use to connect their offices together. The flaw, tracked as CVE-2026-76504 and rated 9.8 out of 10 on the CVSS severity scale, affects Cisco Catalyst SD-WAN Manager. It lets a remote attacker slip past a login check and gain administrator-level access to a protected management API. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has already added it to its Known Exploited Vulnerabilities (KEV) catalog and gave federal agencies until October 3, 2026 to fix it.
Continue reading
  43 Hits

Critical Citrix NetScaler Zero-Days Are Under Active Attack: What Your Business Needs to Do This Week

server-room-closeup-critical-error

A pair of critical, unauthenticated zero-day vulnerabilities in Citrix NetScaler are being actively exploited right now and with roughly 23,000 internet-exposed devices worldwide, this is a "patch today, not next sprint" moment that shows exactly why continuous vulnerability management can't be a once-a-quarter checkbox for any growing business.

Continue reading
  125 Hits

Cybersecurity Threat Advisory: ScreenConnect Security Alert: What Businesses Need to Know About CVE-2026-84869

Threat-Advisory-Banner3

Threat update

A newly disclosed security issue affecting ConnectWise ScreenConnect could allow files to be transferred and executed during an active remote-support session without the authorization or confirmation normally expected in certain circumstances. ConnectWise has released ScreenConnect 26.6.5 to address the vulnerability, identified as CVE-2026-84869, and recommends affected organizations update as soon as possible.  

Continue reading
  280 Hits

Urgent N-central Hotfix: What Businesses Need to Know About the September 2026 Security Update

N-able N-central Hotfix 2026.3
If your IT provider or internal technology team uses N-able N-central, there is a new security update you should know about.

N-able released N-central 2026.3 Hotfix 3 on September 5, 2026, to address two high-severity security vulnerabilities. The flaws could allow an unauthorized person to bypass authentication controls and potentially gain full access to the N-central platform.
Continue reading
  353 Hits

Top Breaches Cost ($) of 2024

HEALTHCARE
FINANCIAL
INDUSTRIAL
TECHNOLOGY
ENERGY
Source: IBM Cost of a Data Breach Report 2024