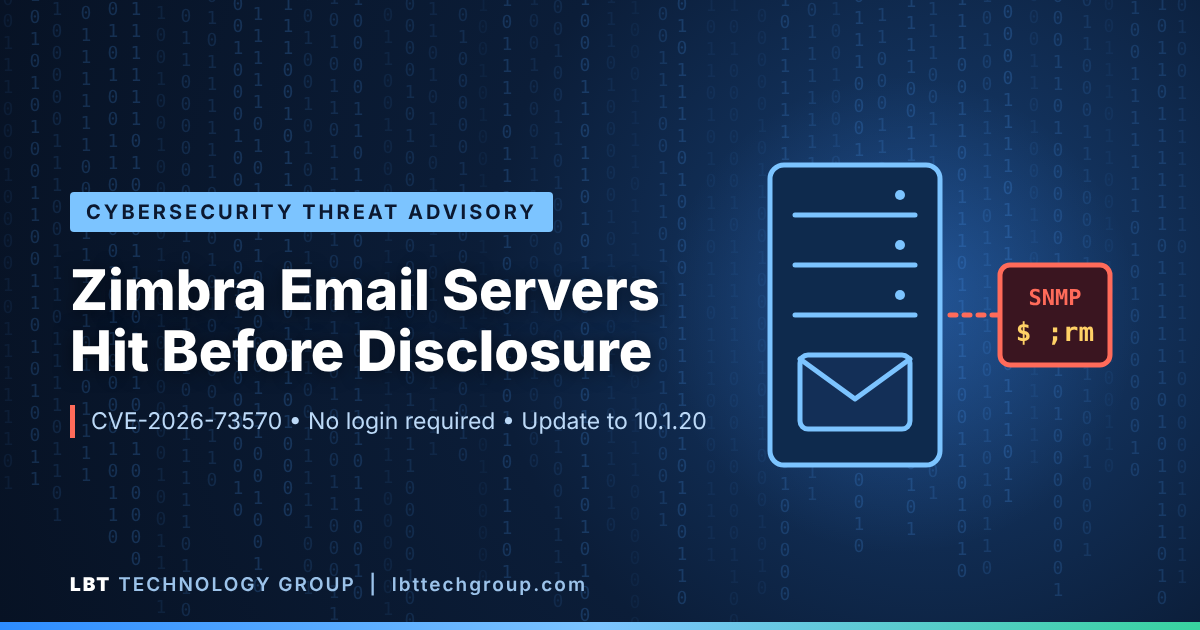
A fix for a critical Zimbra email server flaw was available for more than three weeks before the public was told about it, and attackers used that time. Microsoft Threat Intelligence reports that threat actors exploited CVE-2026-73570 (CVSS 8.9), an unauthenticated operating system command injection vulnerability in the Zimbra Collaboration Suite, for weeks before it was disclosed. The Shadowserver Foundation counted 274 compromised Zimbra servers in a single recent week.
396 Hits