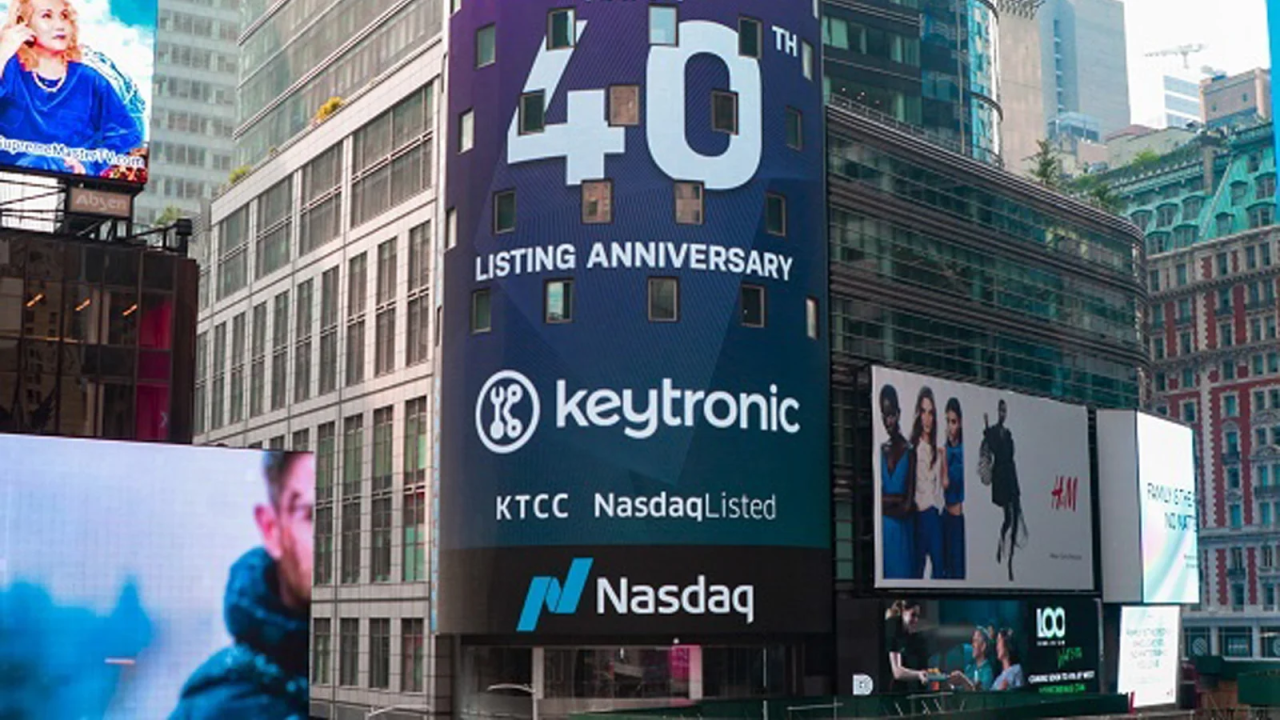
PCBA manufacturing giant Keytronic is warning it suffered a data breach after the Black Basta ransomware gang leaked 530GB of the company's stolen data two weeks ago.

PCBA manufacturing giant Keytronic is warning it suffered a data breach after the Black Basta ransomware gang leaked 530GB of the company's stolen data two weeks ago.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a high-severity Windows vulnerability abused in ransomware attacks as a zero-day to its catalog of actively exploited security bugs.
A recent Microsoft Outlook client zero-click remote code execution (RCE) vulnerability, CVE-2024-30103, has a CVSS score of 8.8.
American financial services holding company Globe Life says attackers may have accessed consumer and policyholder data after breaching one of its web portals.
Google users have been targeted with a typosquatted attack when searching Advanced IP Scanner. When searching for this free network scanner for Windows, users are served with an exploited version of Advanced IP Scanner that injects a CobaltStrike Beacon into the parent process's address space.
A Veeam Backup Enterprise Manager (VBEM) security vulnerability, CVE-2024-29849, can pose serious risks for organizations. Users are advised to update their VBEM to the latest version immediately.
Internal source code and data belonging to The New York Times was leaked on the 4chan message board after being stolen from the company's GitHub repositories in January 2024, The Times confirmed.
LastPass says its almost 12-hour outage yesterday was caused by a bad update to its Google Chrome extension.
British auction house Christie's is notifying individuals whose data was stolen by the RansomHub ransomware gang in a recent network breach.
Frontier Communications is warning 750,000 customers that their information was exposed in a data breach after an April cyberattack claimed by the RansomHub ransomware operation.
A new PHP for Windows remote code execution (RCE) vulnerability has been disclosed, impacting all releases since version 5.x, potentially impacting a massive number of servers worldwide.
A new ransomware operation named 'Fog' launched in early May 2024, is using compromised VPN credentials to breach the networks of educational organizations in the U.S.
Palo Alto Networks has recently disclosed a critical zero-day vulnerability, CVE-2024-3400, within its PAN-OS operating system. The flaw, found in the GlobalProtect Gateway, is currently under active exploitation. Additionally, the threat actors behind RedTail cryptocurrency mining malware have added this vulnerability to its exploit arsenal, further intensifying the threat.
Threat actors claim to be selling 3TB of data from Advance Auto Parts, a leading automotive aftermarket parts provider, stolen after breaching the company's Snowflake account.
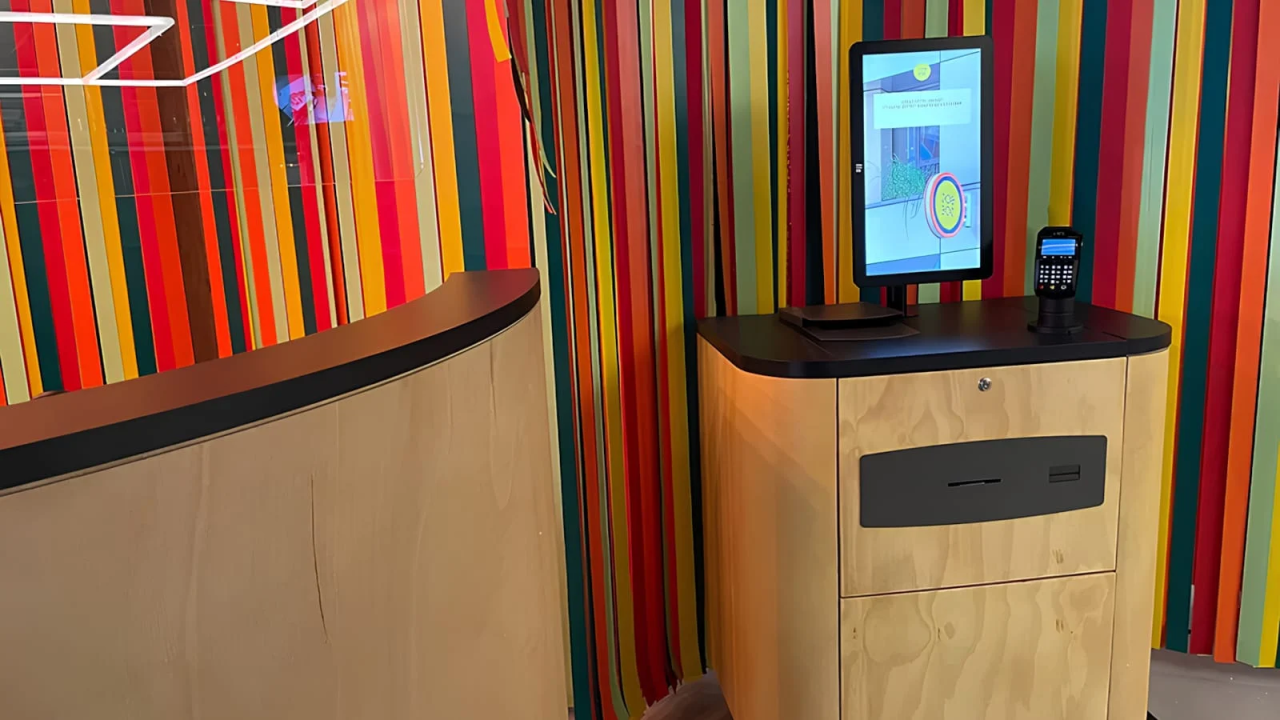
Ariane Systems self check-in systems installed at thousands of hotels worldwide are vulnerable to a kiosk mode bypass flaw that could allow access to guests' personal information and the keys for other rooms.
ShrinkLocker is a recent ransomware strain that leverages a legitimate Windows encryption feature, BitLocker, to lock victims out of their devices. It shrinks the partition, increasing the impact of the attack.
There has been active exploitation of a critical operating system (OS) command injection vulnerability, known as CVE-2017-3506, found in the Oracle WebLogic Server. The impact can be severe, ranging from financial loss to reputational damage.
A new critical command injection vulnerability, CVE-2024-23108, was found in Fortinet's FortiSIEM solution. This vulnerability poses significant risks to organizations using the solution.
Hackers are utilizing code from a Python clone of Microsoft's venerable Minesweeper game to hide malicious scripts in attacks on European and US financial organizations.
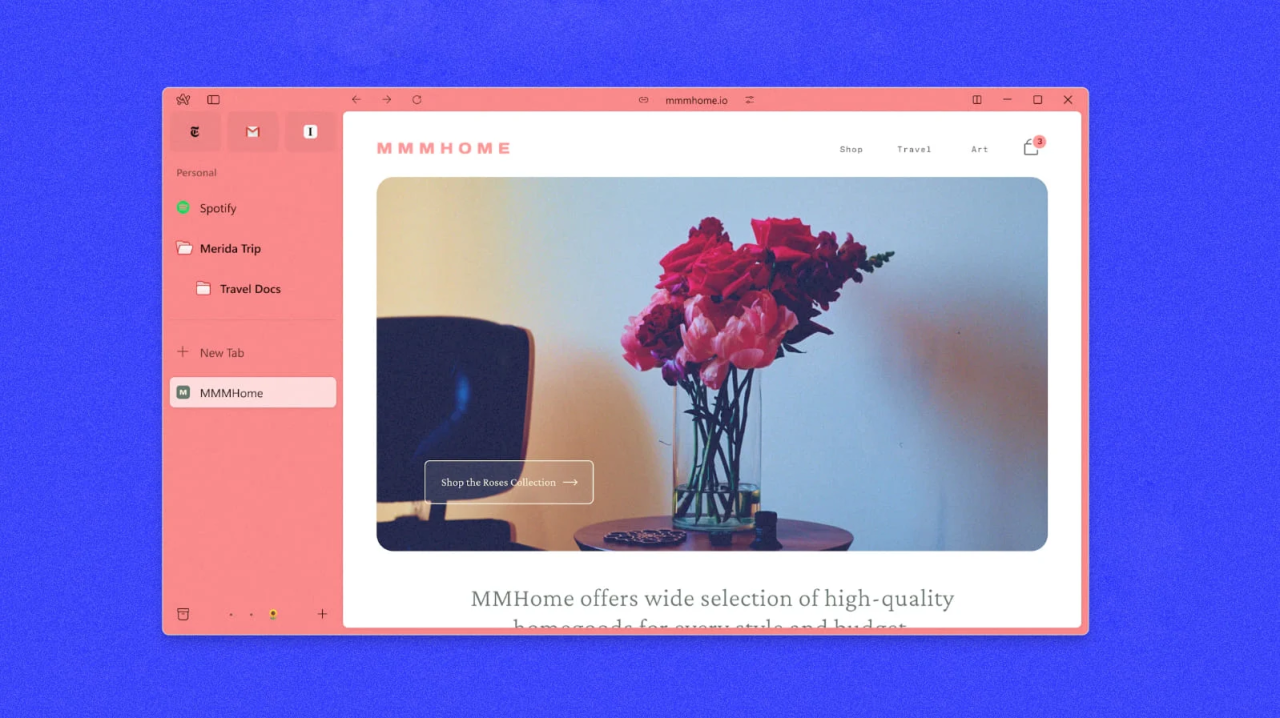
A new Google Ads malvertising campaign, coinciding with the launch of the Arc web browser for Windows, was tricking people into downloading trojanized installers that infect them with malware payloads.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.